Browser Fingerprints
What is browser fingerprinting, and what can a website actually read?
A plain explanation of the signals a page script can read, which ones identify you, and which ones only look like they do.
Canvas fingerprinting explained: why two identical browsers draw different pixels
How a canvas hash is made, why it varies between machines, and what browser noise does to it.
WebRTC leaks: why your real address can show even behind a proxy
What ICE candidates are, how a STUN request exposes an address, and what the browser hides by default now.
Time zone mismatch: the cheapest consistency check on the web
Why a page compares the time zone of your address with the one your browser reports, and what makes them disagree.
User-Agent strings and Client Hints: what they reveal and what was frozen
How the user agent evolved, what is still in it, and how Client Hints changed the rules.
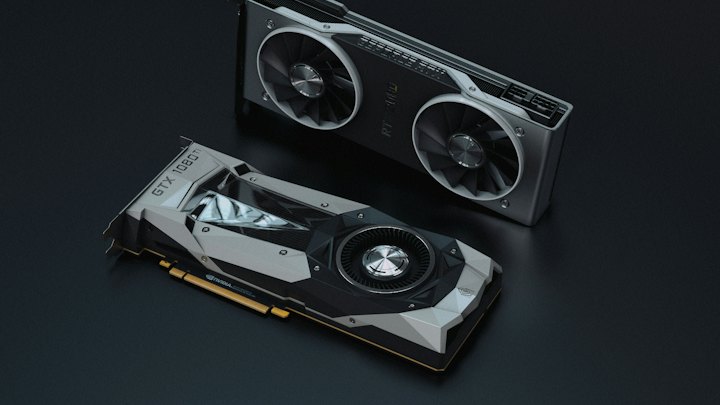
WebGL renderer strings and hardware signals: how much your GPU says about you
What the unmasked renderer, CPU thread count, device memory and screen geometry add to a fingerprint.
Audio fingerprinting without a microphone
How an OfflineAudioContext produces a stable number from your audio stack, and why it never records anything.
Browser Fingerprinting: What Sites Actually Read
A field-by-field tour of the values a website collects, from canvas and WebGL to audio, fonts, screen and timezone, and why a coherent identity beats a randomised one.